Note: This article discusses F-35 cybersecurity risks using publicly available information. It does not provide hacking steps, exploit methods, or classified technical details.
Introduction: When a Fighter Jet Becomes a Flying Data Center
The F-35 Lightning II is not just a stealth fighter. It is a flying sensor platform, a battlefield data hub, a software-defined weapons system, anddepending on whom you aska very expensive computer with wings. That last description is a little unfair to the aircraft, but it captures why the phrase F-35 hacking vulnerability keeps appearing in defense discussions.
Modern air combat is no longer only about speed, altitude, missiles, or radar cross-section. It is about data. The F-35 collects information from its sensors, shares it with other aircraft and commanders, relies on software for mission systems, and depends on a vast digital logistics ecosystem to stay ready for flight. That makes the jet powerful. It also makes cybersecurity a central part of its survivability.
To be clear, public evidence does not show that hostile hackers can simply “take over” an F-35 in midair like a Hollywood villain sipping coffee in a basement. Real military systems are segmented, tested, hardened, and protected by layers of operational security. Still, the F-35 program has faced repeated public scrutiny over cyber risk, especially around its logistics and sustainment systems, software complexity, supply chain, and historical cyber espionage incidents. In short: the aircraft may be stealthy to radar, but its digital ecosystem is impossible to hide from cybersecurity debate.
Why the F-35 Is Cybersecurity-Sensitive
The F-35 is often called a fifth-generation fighter, but “fifth-generation” is not just a cool label for aircraft posters. It means the jet combines stealth, advanced sensors, sensor fusion, electronic warfare, networked communications, and software-heavy mission systems. Those capabilities help pilots see more, decide faster, and share information across the battlefield.
That digital sophistication creates a paradox. The same connectivity and automation that make the F-35 valuable also expand the number of systems that must be protected. Aircraft software, maintenance laptops, portable memory devices, mission planning tools, training systems, contractor networks, supply-chain systems, and logistics servers all become part of the broader security picture.
In older aircraft, a maintenance problem might involve a wrench, a manual, and someone muttering at a hydraulic line. With the F-35, the maintenance environment includes diagnostic data, software updates, cloud-like sustainment workflows, and databases that track parts, repairs, training, and aircraft health. The wrench is still there, but now it has a login screen nearby.
The Big Concern: ALIS and ODIN
Much of the public conversation about F-35 cybersecurity vulnerabilities centers on the aircraft’s logistics backbone. The original system, known as the Autonomic Logistics Information System, or ALIS, was designed to support operations, maintenance, mission planning, supply-chain management, training, and aircraft health monitoring. It was meant to make the F-35 easier to sustain by helping crews predict problems, order parts, and keep aircraft available.
In practice, ALIS became one of the program’s most criticized elements. Government oversight reports described it as complex, central to operations, and affected by data accuracy problems, usability issues, workarounds, and modernization challenges. That matters because a logistics system is not glamorous, but it is decisive. A stealth fighter that cannot be maintained efficiently is less of a warfighting asset and more of a very dramatic lawn ornament.
The Department of Defense began moving from ALIS toward a newer system called ODIN, short for Operational Data Integrated Network. ODIN was intended to reduce maintainer workload, improve mission capability rates, and allow faster software updates. The transition, however, has not been as simple as swapping an old phone for a newer one and pretending the charger situation is under control. Public test reports have noted continuing concerns about cyber survivability testing, software maturity, and the need to correct deficiencies before fully rehosting legacy software on the newer architecture.
What “Hacking Vulnerability” Really Means Here
When readers hear “F-35 hacking vulnerability,” they may imagine someone remotely steering the aircraft. That is not the most realistic way to understand the risk. In public discussions, the more credible concerns usually fall into several categories:
1. Data Theft and Cyber Espionage
One of the most widely reported cyber issues involving the F-35 program was not about controlling an aircraft, but about stealing information. Public reporting has described past cyber intrusions in which design and electronics-related data associated with the Joint Strike Fighter program were allegedly taken. U.S. officials have stated in public reporting that the most sensitive classified information was not stolen, but even less-sensitive technical data can still help adversaries reduce research costs, improve their own systems, or develop countermeasures faster.
2. Logistics Disruption
A cyberattack does not need to touch flight controls to matter. If an adversary could corrupt maintenance data, delay parts, interfere with mission planning tools, or reduce confidence in aircraft health information, the result could be fewer jets ready to fly. In military terms, readiness is not an abstract spreadsheet metric. It determines whether aircraft are available when commanders need them.
3. Software Supply-Chain Risk
The F-35 depends on a wide industrial base, including prime contractors, subcontractors, software developers, hardware suppliers, and allied partners. Every major defense supply chain is a potential target for espionage or sabotage. Attackers often prefer weaker links, because the front gate of a military program is usually heavily guarded while a smaller supplier may have fewer resources.
4. Mission Data Integrity
The F-35 relies on mission data files and threat libraries to identify, classify, and respond to battlefield signals. If data integrity were compromised, the aircraft’s decision-support environment could be affected. Public sources do not provide operational details, and they should not. But at a high level, any system that depends on trusted data must protect that data from tampering.
5. Testing Gaps
Cyber survivability testing is difficult because realistic tests can be disruptive, expensive, and limited by the availability of representative aircraft and systems. Public test evaluations have called for more in-depth testing of the aircraft, ALIS/ODIN, training systems, and simulation environments. That does not mean the F-35 is defenseless. It means the program is still working to prove, improve, and verify cyber resilience across a very large digital ecosystem.
Why the F-35 Is Hard to Secure
Securing the F-35 is not like installing antivirus software and calling it a patriotic afternoon. The program spans U.S. military services, international partners, foreign military sales customers, contractors, depots, bases, ships, software labs, and operational theaters. It includes classified and unclassified data, air vehicles, ground systems, training platforms, and sustainment networks.
The aircraft also evolves continuously. Block upgrades, Technology Refresh programs, new weapons integrations, and software releases add capability but also require testing. Every update must be assessed not only for whether it works, but whether it remains secure, stable, and compatible with the rest of the enterprise.
Another challenge is age. Some parts of the original logistics architecture were designed years before today’s cyber threat environment matured. Systems built in one era often need major redesigns to meet the demands of another. That is one reason ODIN exists: to move toward a more modern, agile, and manageable sustainment environment.
Is the F-35 Actually Hackable?
The honest answer is: every complex digital system has cyber risk, but “hackable” is too vague to be useful. A smartphone, hospital network, satellite system, aircraft maintenance database, and fighter jet all have different threat models. The important question is not whether risk exists. It does. The important question is whether the system can detect, resist, recover from, and continue operating through cyber pressure.
For the F-35, the most realistic public concerns involve cyber espionage, sustainment disruption, software deficiencies, data integrity, and supply-chain security. These are serious issues, but they are not the same as saying an enemy can casually hijack an aircraft. Military aircraft are designed with layers of separation, validation, access control, and operational procedures. Still, because the F-35 is so software-dependent, cybersecurity must be treated as a mission requirement rather than an IT side quest.
Specific Public Examples That Shaped the Debate
Several public examples explain why the topic remains controversial. First, older reporting about cyber espionage against the Joint Strike Fighter program raised alarms about stolen design-related data. Even if classified flight-critical systems were not compromised, the theft of technical information can help competitors understand design choices and accelerate their own development.
Second, GAO reports on ALIS highlighted the importance of the logistics system to F-35 operations and described persistent challenges including data accuracy, deployment issues, training gaps, and the need for better performance tracking. When a logistics platform is tied to maintenance, parts, mission planning, and aircraft health, weaknesses in that platform become operational concerns.
Third, DOT&E reports have repeatedly emphasized the need for more robust cyber survivability testing. Public recommendations have included deeper testing of the air vehicle, ALIS/ODIN, training systems, and simulation environments, along with timely correction and verification of cyber deficiencies. That language is careful, bureaucratic, and very government-report-ish, but the meaning is plain: test harder, fix faster, and prove the fixes.
The Readiness Connection
Cybersecurity and readiness are linked. If maintenance data is unreliable, if software updates are delayed, if supply-chain systems are slow, or if cyber testing reveals unresolved deficiencies, aircraft availability can suffer. GAO has reported declining mission-capable and full mission-capable rates across the F-35 fleet in recent years, while sustainment costs have continued to rise. Not every readiness problem is a cyber problem, of course. Spare parts, depot capacity, contractor incentives, software delays, and maintenance workload all play roles. But cyber resilience is part of the same readiness puzzle.
This is why the F-35 hacking vulnerability conversation should not be reduced to spy-movie scenarios. The real issue is whether a digital warplane can remain dependable under stress. In modern conflict, an adversary may not need to destroy an aircraft if they can slow maintenance, confuse logistics, steal data, or exploit weak links before the first sortie begins.
How the F-35 Program Can Reduce Cyber Risk
Build Cybersecurity Into Every Upgrade
Cybersecurity cannot be bolted on after development like a spoiler on a sedan. Every software release, hardware refresh, logistics update, and weapons integration should include security design, testing, and verification from the beginning.
Improve Realistic Cyber Survivability Testing
Testing should use representative systems whenever possible, including hardware- and software-in-the-loop environments. Simulations should also be able to model cyber effects during mission rehearsals so operators can understand how degraded systems behave.
Strengthen Supply-Chain Security
The F-35 enterprise depends on thousands of people and companies. Supplier cybersecurity, component integrity, secure refurbishment practices, and contractor accountability are essential. The strongest aircraft in the world can still be affected by a weak vendor password, which is a sentence no general wants embroidered on a pillow.
Protect Maintenance and Mission Data
Data must be accurate, authenticated, and monitored. Maintenance records, parts information, mission files, and diagnostic outputs should be protected against tampering and checked for anomalies. Trust is useful; verification is better.
Reduce Dependence on Fragile Central Systems
Military operations should be able to continue when networks are degraded or disconnected. The F-35 program has already faced questions about operating without full access to central logistics systems. Resilience means crews can keep aircraft flying even when perfect connectivity is unavailable.
What This Means for Pilots, Maintainers, and Commanders
For pilots, cyber resilience means confidence that the aircraft’s mission systems, displays, sensors, and data are behaving as expected. For maintainers, it means diagnostic tools and logistics software support the mission instead of creating extra work. For commanders, it means cyber risk is factored into readiness, deployment planning, and operational assumptions.
For taxpayers, it means the most expensive weapons program in U.S. history must be judged not only by aircraft performance, but by the health of the digital ecosystem around it. A jet can have world-class sensors and still be held back by software delays, sustainment bottlenecks, or unverified cyber fixes.
Experience-Based Lessons From the F-35 Cybersecurity Debate
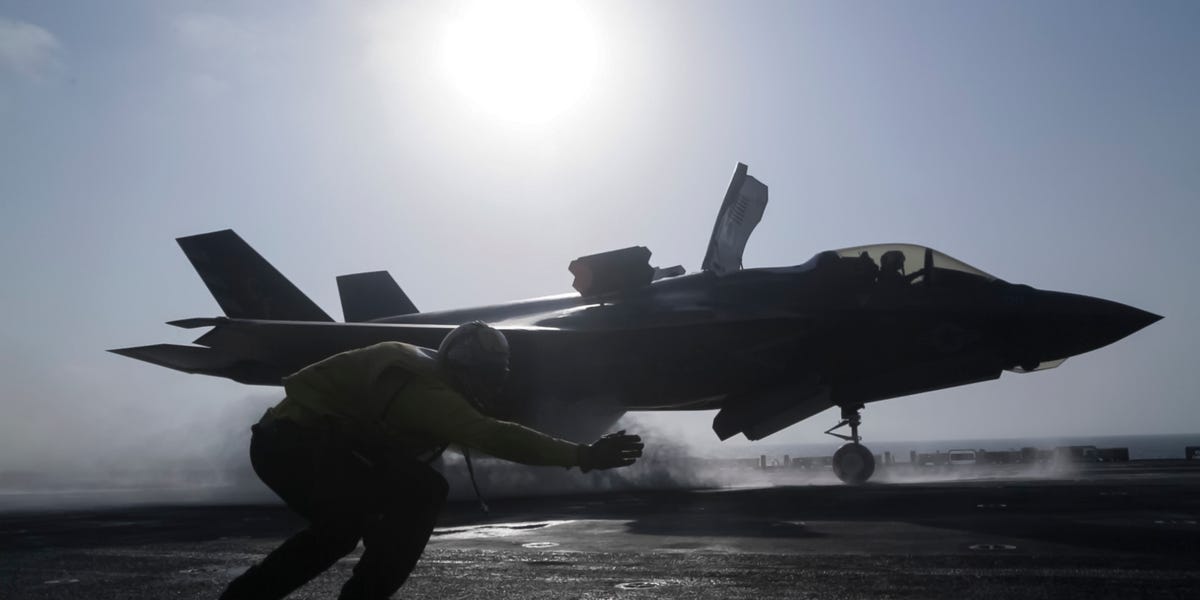
Anyone who has worked around complex technology learns one lesson quickly: the flashy part is rarely the whole story. In the F-35’s case, the flashy part is obvious. It is the stealth profile, the helmet display, the vertical landing variant, the weapons bay, and the dramatic runway photos that make aviation fans whisper, “Yes, please.” But the less glamorous sidethe databases, maintenance workflows, update cycles, spare-parts systems, and cybersecurity controlsis what keeps the aircraft useful day after day.
The first practical lesson is that cybersecurity is not separate from operations. In a modern fighter program, cyber hygiene affects sortie generation, mission confidence, and long-term sustainment. A corrupted maintenance record may not look as dramatic as a missile launch, but it can still delay a mission. A late software patch may not make headlines, but it can limit capability. A supplier breach may happen far from the flight line, yet still expose information that helps an adversary.
The second lesson is that complexity must be managed aggressively. The F-35 was designed to do many things for many users across multiple services and allied nations. That ambition brings enormous capability, but it also creates integration risk. When one system supports maintenance, supply chain, training, prognostics, mission planning, and data exchange, small weaknesses can ripple outward. The lesson for any organization is simple: the more connected the system, the more disciplined the governance must be.
The third lesson is that modernization is never finished. ALIS was criticized for years, and ODIN was introduced as a better path forward. But moving from one architecture to another does not magically erase legacy problems. Old software, old assumptions, and old workflows often travel inside the moving boxes. Successful modernization requires clear requirements, realistic schedules, user feedback, independent testing, and the humility to admit when “almost done” actually means “please bring snacks, this meeting will be long.”
The fourth lesson is that public cyber discussions need precision. Saying “the F-35 can be hacked” is too broad and often misleading. A better discussion asks what could be targeted, how likely the risk is, what operational effect it might create, and what mitigations exist. Data theft, logistics disruption, supply-chain compromise, and mission-system interference are different problems. Treating them as one giant cyber monster may be exciting, but it does not help anyone fix the real issues.
The final lesson is that resilience matters as much as prevention. No serious cyber program assumes perfect defense. The goal is to prevent what can be prevented, detect what gets through, limit damage, recover quickly, and keep the mission moving. For the F-35, that means tested backup procedures, trusted data flows, trained maintainers, accountable contractors, realistic cyber exercises, and software practices that match the aircraft’s importance.
The F-35’s hacking vulnerability is not a single flaw waiting in a dark corner. It is a broad risk category created by software dependence, global sustainment, networked operations, and the realities of cyber competition. The aircraft remains one of the most advanced combat platforms in the world. But in the twenty-first century, air superiority is no longer only won in the sky. It is also defended in code repositories, logistics networks, test labs, and supply-chain audits. Not as cinematic, perhapsbut absolutely mission critical.
Conclusion: The F-35’s Cyber Risk Is Real, but Not Cartoonish
The F-35 is not doomed because it has cybersecurity concerns. Every advanced military platform has them. The difference is that the F-35 is unusually dependent on software, data, and sustainment networks, making cyber resilience central to its value. The serious risks are less about movie-style remote hijacking and more about espionage, logistics disruption, data integrity, software maturity, supply-chain exposure, and insufficiently representative testing.
The way forward is not panic. It is disciplined engineering, transparent oversight, stronger cyber testing, better contractor accountability, resilient logistics, and continuous modernization. The F-35 was built to survive contested airspace. Now its digital ecosystem must prove it can survive contested cyberspace, too.